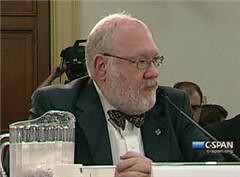
 An expert has given testimony to the US House of Representatives Subcomittee on Commerce, Manufacturing, and Trade during its commencement on hearings on the “unauthorized intrusion” on Sony’s PlayStation Network and Qrocity service, stating Sony knew that their security software was dated and lacked any sort of firewall against hacking.
Cybersecurity expert Dr. Gene Spafford’s testimony stated that security experts discovered discussions on forums that talked about how the PSN’s security was lacking. The threads revealed that the network was using old versions of the Apache Web server software, which “was unpatched and had no firewall installed.”
Worse, two to three months before the attack, the vulnerability was reported “in an open forum monitored by Sony employees,” but the company took no action to rectify the situation. If the testimony is accurate, Sony could be slapped with a serious criminal negligence charge.
The Sony intrusion alone compromised 100 million accounts both on the PSN and its Qriocity service, according to Spafford. He also cited the total cost of the breach to Sony, credit card companies, and other outfits, at $21 billion. Thieves in credit-card theft forums actually complained that the PSN breach was so great that it was depressing the price of such information by a “factor of five or 10” on the black market.
Spafford didn’t reserve his accusations for Sony, either. He stated that law enforcement is ill-equipped to handle cyberterrorism and cyberthieft. Additionally, most companies are not equipped with enough security measures because “investing in security measures affects the bottom line. They don’t understand the risks involved by not investing in security. … So when they are hit, they pass that cost along to their customers, and to the rest of society.” In other words, a classic case of being penny wise and pound foolish.
Spafford’s proposed solution to future security is to limit the amount of data kept by companies such as Sony and to “age the data” so it expires after a certain time.
C-Span posted the video of the testimony here.
(Thanks, GameSpot.)
 The patience of PlayStation 3 owners is
 While full PlayStation Network service is expected to return by May 31, Eurogamer is
One of the better pieces on the PSN fiasco that I’ve read, congrats Jonah!
I had two jobs as a programmer; in both cases, interacting with the IT department felt more like interacting with Dilbert’s “Information prevention department”, ran by Catbert. They even wanted (and succeeded in one place) to push a “Service Level Agreement”: it’ll take two days to create a new password for this, seven days to do that etc.
They just don’t put enough heart in it.
To be fair, my very first job though was … in the IT department of my college! IT work is hard. If you screw up (and we did screw up sometimes), you could kiss your weekend goodbye . Usually, we’d investigate the issue that very evening, then tried to implement it either during the next day, or, at worst, if the computers we’d want to alter were being in use, in the weekend.
The lessons I learned there is that: (1) you must react quickly and (2) if you put a bit of your heart into your work, you can get surprisingly good results.
Nice find on the “depressing the price of such information by a “factor of five or 10? on the black market”. I guess the PSN issue is the equivalent of flooding the market with products 🙂
@” limit the amount of data kept by companies such as Sony and to “age the data””
This is security basics. If you don’t want to be responsible for safekeeping secret information, then don’t store secret information on your servers. Period.