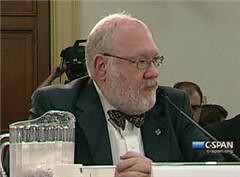
 An expert has given testimony to the US House of Representatives Subcomittee on Commerce, Manufacturing, and Trade during its commencement on hearings on the “unauthorized intrusion” on Sony’s PlayStation Network and Qrocity service, stating Sony knew that their security software was dated and lacked any sort of firewall against hacking.
Cybersecurity expert Dr. Gene Spafford’s testimony stated that security experts discovered discussions on forums that talked about how the PSN’s security was lacking. The threads revealed that the network was using old versions of the Apache Web server software, which “was unpatched and had no firewall installed.”
Worse, two to three months before the attack, the vulnerability was reported “in an open forum monitored by Sony employees,” but the company took no action to rectify the situation. If the testimony is accurate, Sony could be slapped with a serious criminal negligence charge.
The Sony intrusion alone compromised 100 million accounts both on the PSN and its Qriocity service, according to Spafford. He also cited the total cost of the breach to Sony, credit card companies, and other outfits, at $21 billion. Thieves in credit-card theft forums actually complained that the PSN breach was so great that it was depressing the price of such information by a “factor of five or 10” on the black market.
Spafford didn’t reserve his accusations for Sony, either. He stated that law enforcement is ill-equipped to handle cyberterrorism and cyberthieft. Additionally, most companies are not equipped with enough security measures because “investing in security measures affects the bottom line. They don’t understand the risks involved by not investing in security. … So when they are hit, they pass that cost along to their customers, and to the rest of society.” In other words, a classic case of being penny wise and pound foolish.
Spafford’s proposed solution to future security is to limit the amount of data kept by companies such as Sony and to “age the data” so it expires after a certain time.
C-Span posted the video of the testimony here.
(Thanks, GameSpot.)
In before Herr_Alien. 🙂
Come on Paul! How many podcasts are you going to miss?
@GOG says customers hate DRM: Of course they do! Just like you said, DRM only hurts the customers and not the pirates. And yes, please bring back games filled with physical content, I would love to have stuff like that.
@QOTW: Sorry, don’t know of any DRM that I could tolerate. I know that pirates shouldn’t be accepted, but unfortunately there’s nothing that can be done about them.
@DynamicJul
😀 Actually it is a nice change. The time zone difference usually works in my favor (Eastern Europe), but it’s not completely impossible for somebody from US to get in first.
@EA forum bans cause game bans:
So apparently they didn’t fix the issue yet … they’re still using one database to handle the authentication for both systems.
If you think of it, you don’t even need two databases with the same user/password data, you only need separate databases to store forum bans from whole-account bans.
Correcting the bug should not be that difficult and it will make a huge impact for the better.
@piracy’s up 20% in past 5 years:
Games for free? Who would think this would ever be a lucrative business? 😛
I for one would pirate the shit out of Assassin’s Creed 2, just to point out that intrusive DRM is not ok. I’m not that much into that kind of game though, so …
@GOG sez customers hate DRM
And for good reason. As long as the code reaches the client, any DRM measures in it will be bypassed. Not might be bypassed, not could be bypassed, WILL be bypassed.
As for physical content, well, you still have those Deluxe editions.
@Steam user database cracked:
Not the best of the possible news. I don’t like to have the credit card info stored on servers, and in my envision of an online store, the credit card info is never stored. Yes, with every purchase you would need to type in the number again, but unless you check out very often (instead of putting more items in the basket then checking out) it should be quite ok.
@QOTW:
Steam, and the regular CD-key.
Jonah, regarding DynamicJul’s comment, I think you mean pseudo-code. And it’s not really about pseudo-code; as long as you know (1) what you want the program to do and (2) how to do it in one language, it will be easy to get the same thing from another language. The main hurdle in all software companies is not about learning a new language, is more about figuring out what the software you’re making is supposed to do.
Actually my time zone is GMT +1 so it’s the same. Also, I forgot to mention that my country doesn’t have things such as ‘Microsoft offices’ or ‘video game shops’ so I have to buy everything off the internet and it isn’t possible to fix an Xbox 360 over the internet.
Wait… taking fallout 3 apart and putting it back together again? This time it’s a brand new engine, so even if they learnt some stuff from the previous games, it’s not like they could reuse that much this time as they have done between previous games.